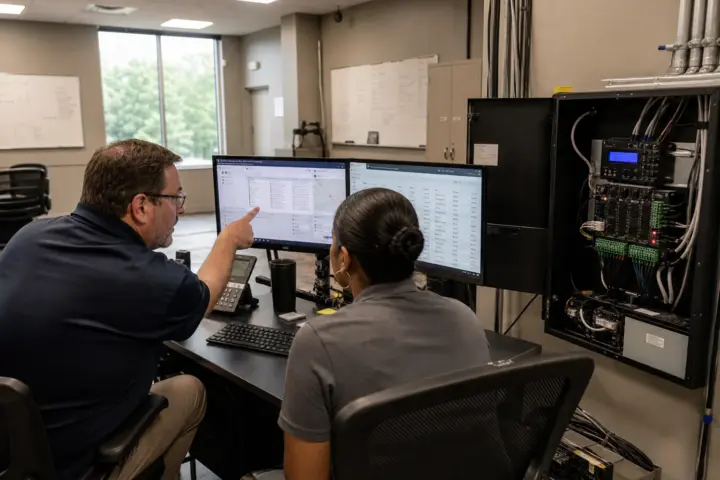

Access control reports are useful when they answer an operational question. A database containing thousands of door events is not automatically intelligence. Businesses need a small set of exceptions, reliable timestamps and a clear process for reviewing what matters.
Reporting should be evaluated while comparing access control systems, not after installation. Ask vendors to demonstrate the exact reports administrators will use.
Understand the events behind a report
Common events include access granted, access denied, door forced open, door held open, reader offline, controller communication loss and administrator changes. Each event needs context: the door, user, credential, timestamp and system status. If clocks are wrong or door names are vague, investigation becomes slower.
Start with exception reports
Most organizations do not need to review every successful entry. Focus first on forced doors, excessive held-open time, repeated denied attempts, inactive readers and credentials used outside expected schedules. Set thresholds carefully so ordinary operations do not generate constant alerts.
Review credentials and users regularly
Useful user reports identify expired credentials, accounts that have not been used, credentials without owners and people assigned to broad permission groups. Review processes should include role changes, terminations, temporary users and duplicate accounts.

Protect administrator activity
Audit logs should show who created users, changed permissions, modified schedules, acknowledged alarms or exported records. Limit administrative accounts, use individual logins and enable stronger authentication where available. A shared administrator account makes accountability difficult.
Define an investigation workflow
- Preserve the relevant time range and note the reported incident time.
- Verify the door name, reader status and controller clock.
- Review credential events before and after the incident.
- Compare related video or alarm records when available.
- Document conclusions, unresolved questions and corrective action.
Access events do not prove identity by themselves. Credentials can be shared, doors can be held and people can follow an authorized user. Treat reports as evidence within a broader review.
Set retention and export rules deliberately
Retention should reflect operational, legal, insurance and policy needs. Confirm whether records remain available after a subscription ends and whether exports include usable timestamps, door names and user identifiers. Protect exported data because it can reveal employee routines.
Build a multi-site reporting structure
Standard door names, event definitions and permission groups make reports easier to compare across locations. Decide which administrators can view one site, a region or the entire organization. Central visibility can help, but local staff still need a clear escalation path.
Questions to ask during a software demonstration
- Can forced-open, held-open and offline events be filtered by door and time?
- Can alerts use different thresholds and recipients?
- Does the audit log record permission and schedule changes?
- How long are events retained, and can they be exported?
- How does reporting work during and after an outage?
- Can administrators be restricted by site and role?
- Which reports require added licenses or subscriptions?
The cloud versus on-premises comparison explains how hosting affects administration and retention. Use the buyer’s guide to compare software terms, then request access control pricing for the doors and reporting requirements you have documented.
Frequently asked questions
How often should access reports be reviewed?
Critical alerts may need immediate response, while user and credential reviews can follow a documented weekly, monthly or quarterly schedule based on risk and staffing.
Can access control reports be used for employee attendance?
Door events show credential activity, not guaranteed work time or identity. Organizations should consider policy, employment and privacy requirements before using them for another purpose.
What is the difference between an alert and a report?
An alert is usually a near-real-time notification triggered by a rule. A report summarizes or filters stored events for review and investigation.
Do cloud systems keep events forever?
Not necessarily. Retention varies by platform, plan and contract. Confirm limits, export rights and what happens when service ends.